Ecosystem
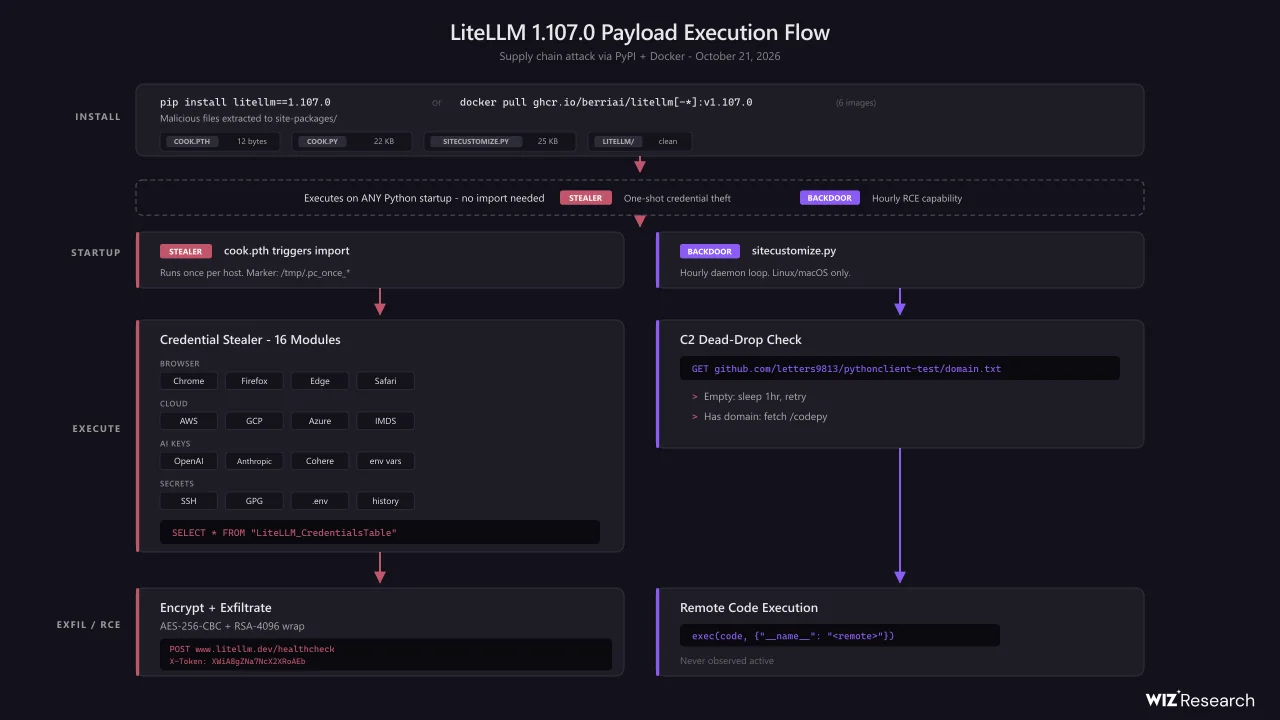
LiteLLM 1.107.0 shipped a credential stealer: rollback alone is not the fix
Developing 2 sources
LiteLLM says its public 1.107.0 Python wheels and selected container tags carried credential-stealing malware on October 21; the artifacts were removed while the intrusion investigation continues.
What happened lately
LiteLLM confirms that public release 1.107.0 was compromised on October 21, 2026. Its report identifies all seven PyPI wheels and selected Docker Hub and GHCR tags, while saying its private enterprise registry was unaffected. The source tag itself did not contain the malicious files: the release pipeline built artifacts from an attacker-controlled lookalike repository.
Wiz describes Python-startup hooks that steal browser, cloud and AI provider credentials, plus a second-stage remote loader. LiteLLM’s reconstruction of the initial intrusion remains provisional. Its recommended response includes rebuilding affected environments and rotating reachable secrets, rather than treating a package rollback as complete remediation.